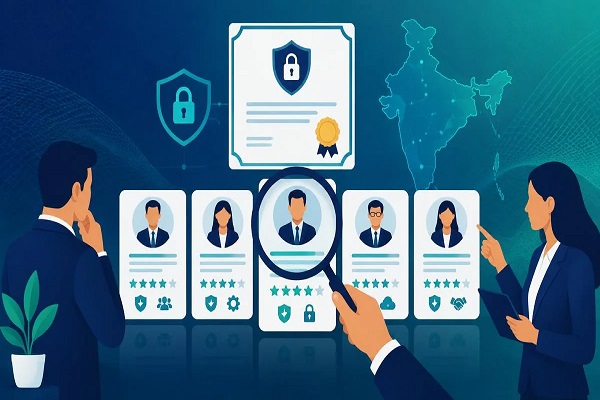
Information security has become a major priority for businesses handling sensitive customer information, financial records, and confidential business data. As cyber threats continue to evolve, organizations need reliable security frameworks to protect their digital assets. Choosing the best ISO 27001 consultants in India can help businesses establish effective security practices and achieve internationally recognized certification. With professional guidance from CyberWave GRC, organizations can strengthen their information security management systems, identify potential risks, improve compliance, and build customer confidence. A structured approach also helps businesses maintain security standards while supporting long-term growth.
Understanding the Importance of ISO 27001 Certification
ISO 27001 is an internationally recognized standard for Information Security Management Systems (ISMS). It provides organizations with a structured framework for identifying, managing, and reducing information security risks. Rather than focusing only on technical protection, this standard addresses people, processes, technology, and organizational responsibilities.
Businesses across industries can benefit from implementing ISO 27001. It helps protect confidential information, improve internal controls, and establish consistent security procedures. Furthermore, certification demonstrates an organization’s commitment to protecting sensitive information.
Working with the best ISO 27001 consultants in India makes implementation more organized. Experienced consultants understand certification requirements and help businesses develop security policies that match their operational needs. Consequently, organizations can avoid unnecessary delays and prepare more effectively for certification audits.
Why Businesses Need the best ISO 27001 consultants in India
Implementing an information security management system requires careful planning, technical knowledge, and continuous monitoring. Without professional assistance, organizations may struggle to understand documentation requirements, identify security gaps, and establish suitable controls.
The best ISO 27001 consultants in India provide practical guidance throughout the implementation process. They assess existing security practices, recommend improvements, and help businesses align their operations with ISO 27001 requirements.
Here are some important benefits of professional consulting:
- Risk identification: Consultants identify potential threats and vulnerabilities affecting business information.
- Regulatory alignment: They help organizations understand relevant security and compliance obligations.
- Documentation support: Proper policies, procedures, and records are developed for effective implementation.
- Audit preparation: Businesses receive guidance to prepare for internal and external audits.
- Continuous improvement: Organizations establish processes for monitoring and improving security performance.
Moreover, professional consulting reduces confusion and helps internal teams understand their security responsibilities.
How CyberWave GRC Supports ISO 27001 Implementation
CyberWave GRC helps organizations approach information security compliance through structured planning and practical implementation support. Every business has different operational requirements, so an effective ISMS should reflect its actual risks, processes, and business objectives.
The best ISO 27001 consultants in India understand that successful implementation involves more than preparing documents. It requires developing a security-focused organizational culture.
CyberWave GRC supports businesses through important implementation activities, including understanding certification requirements, evaluating existing controls, identifying security gaps, developing necessary documentation, and preparing teams for audits.
Additionally, organizations receive guidance on implementing appropriate security controls. This structured approach helps businesses establish clear responsibilities and maintain consistent information security practices.
Essential Steps in the ISO 27001 Certification Process
Achieving ISO 27001 certification involves several important stages. Understanding these stages helps organizations prepare resources and manage implementation efficiently.
1. Initial Gap Assessment
The process begins with reviewing existing information security practices against ISO 27001 requirements. Consultants identify weaknesses and recommend corrective actions.
2. Defining the ISMS Scope
Organizations determine which departments, systems, locations, and information assets fall within the ISMS scope. A clearly defined scope makes implementation more manageable.
3. Risk Assessment and Treatment
Businesses identify information security threats, evaluate their potential impact, and select suitable risk treatment measures. This stage establishes the foundation of an effective security program.
4. Documentation and Policy Development
Organizations prepare information security policies, procedures, risk registers, and other required records. These documents establish consistent processes and responsibilities.
5. Security Control Implementation
Appropriate controls are introduced to address identified risks. These may include access management, incident response, asset management, employee awareness, and business continuity measures.
6. Internal Audit and Management Review
Internal audits evaluate whether implemented controls operate effectively. Management reviews help leadership assess performance and identify improvement opportunities.
7. Certification Audit
An accredited certification body evaluates the organization’s ISMS. Successful completion of the required audit stages can lead to ISO 27001 certification.
The best ISO 27001 consultants in India help businesses navigate these stages with better planning, documentation, and implementation support.
Key Qualities to Consider When Selecting ISO 27001 Consultants
Selecting an appropriate consulting partner can significantly influence the success of an ISO 27001 project. Businesses should evaluate several factors before making their decision.
First, consider the consultant’s knowledge of ISO 27001 requirements and information security management. Practical industry experience is equally important because different organizations face different security challenges.
Second, evaluate the consulting approach. A suitable partner should explain technical requirements clearly and provide recommendations that align with business operations.
Third, consider documentation expertise, risk management capabilities, audit preparation, and communication practices. Transparent project planning also helps organizations understand responsibilities and implementation timelines.
The best ISO 27001 consultants in India should focus on sustainable compliance rather than temporary certification preparation. This ensures that security practices remain effective after certification.
Strengthening Business Trust Through Information Security
Information security plays an important role in building relationships with customers, partners, and stakeholders. Businesses that demonstrate responsible information management can improve their credibility and strengthen their competitive position.
ISO 27001 provides a recognized framework for demonstrating this commitment. It also encourages employees to follow consistent security practices and understand their responsibilities.
Furthermore, organizations with effective ISMS processes can respond more systematically to security incidents. Regular monitoring, risk assessments, and management reviews support continuous improvement.
By working with the best ISO 27001 consultants in India, businesses can develop security programs that support customer confidence, operational resilience, and long-term business objectives.
HITRUST Readiness Assessment
A HITRUST readiness assessment helps organizations evaluate their existing security and privacy controls against applicable HITRUST CSF requirements. It identifies compliance gaps, reviews current policies and procedures, and highlights areas requiring improvement before a formal assessment. Organizations handling sensitive healthcare information can use this process to understand their security maturity and prepare for certification activities. Proper readiness planning also supports stronger risk management, better documentation, and improved protection of sensitive data. A structured assessment provides businesses with a clearer understanding of their compliance responsibilities and helps establish a practical roadmap for addressing identified weaknesses.
Conclusion
Information security is essential for protecting business information, maintaining customer trust, and supporting sustainable growth. ISO 27001 provides organizations with a structured approach to managing security risks and improving operational controls.
Choosing the best ISO 27001 consultants in India can simplify implementation, improve documentation, and strengthen audit readiness. With CyberWave GRC, organizations can approach compliance through practical guidance, structured assessments, and continuous improvement.
Investing in professional consulting is not simply about achieving certification. It is about establishing a reliable information security management system that protects valuable business assets, supports regulatory compliance, and prepares organizations for evolving cybersecurity challenges.